Trust
We train the drug & alcohol testing industry on privacy and compliance — so we hold our own platform to the same standard. Here is how we protect trainee, employer, and C/TPA tenant data.
About this page
This page describes TestRight Academy’s current general security and privacy practices. It is provided for transparency and does not constitute a certification, independent security audit, SLA, warranty, or contractual security commitment. Specific third-party services and integrations maintain their own security and privacy practices.
Encryption
Connections to TestRight services use HTTPS/TLS encryption in transit.
Access controls
Access is restricted according to application roles and permissions, and multi-factor authentication is required for administrative access.
Data minimization
Logging is configured to avoid recording sensitive content that is not needed for an authorized operational purpose.
Customer separation
Application controls are designed to separate customer records between organizations.
How we protect data
Data protection & encryption
- Connections to TestRight services use HTTPS/TLS encryption in transit; requests to the unencrypted endpoint are redirected to HTTPS.
- Application data is stored within access-controlled infrastructure, outside the public web root, and is not intentionally exposed through public endpoints.
- Credentials and configuration are kept separate from the data they protect.
- We apply least privilege: access to systems and data is limited to what each role or system requires.
Access & authentication
- Authentication credentials are stored using one-way password hashing and access controls, rather than in a recoverable form.
- Multi-factor authentication is required for administrative access. An administrator who has not enrolled in MFA cannot reach administrative functions.
- Access is granted on a least-privilege basis and reviewed over time.
- Public-facing forms use automated bot-protection controls to reduce automated abuse.
Sensitive information & logging
TestRight’s logging practices are designed to minimize unnecessary sensitive information. We configure application logging to avoid intentionally recording payment credentials, drug-test results, medical information, or other sensitive content unless needed for an authorized operational purpose. Where practical, internal identifiers are used instead of directly identifying information.
- Drug-test results and medical information are treated as confidential, and access is restricted according to application roles and permissions.
- We aim to collect only the personal information we need for the service.
Customer separation
Application controls are designed to separate customer records between organizations, so that one organization’s records are not surfaced to another through the application.
Operational security
Monitoring & reviews
- Automated checks run on a recurring schedule and surface error and alert conditions to our team for investigation.
- We periodically review application and infrastructure security configurations.
Backups & continuity
Selected production data — the private application data store, database and key configuration — is backed up on a nightly automated schedule. Backups are encrypted, copies are held off this server, and a rolling set of recent copies is retained. Backup coverage is defined by our current infrastructure backup configuration and is not a guarantee of recovery in every scenario.
Incident response
If we become aware of a security incident affecting your data, we will investigate promptly, work to contain and remediate it, and notify affected customers as required by law.
Privacy & data handling
Data retention
Telemetry records are pruned on a rolling retention window. Other operational records are retained for as long as needed for the service and for our legal and record-keeping obligations.
Privacy requests
You can request access to, correction of, export of, or deletion of your data — email info@osegroupusa.com. Requests are handled subject to legal, contractual, security, backup and record-retention requirements. See our Privacy Policy for details.
Payment processing
Payment-card processing is handled by Stripe. TestRight Academy does not intentionally receive or store full payment-card numbers through its application.
Industry membership
TestRight Academy holds an Associate membership in good standing with the National Drug & Alcohol Screening Association (NDASA), the national trade association for the drug and alcohol testing industry. You can view our member profile on the NDASA member directory.
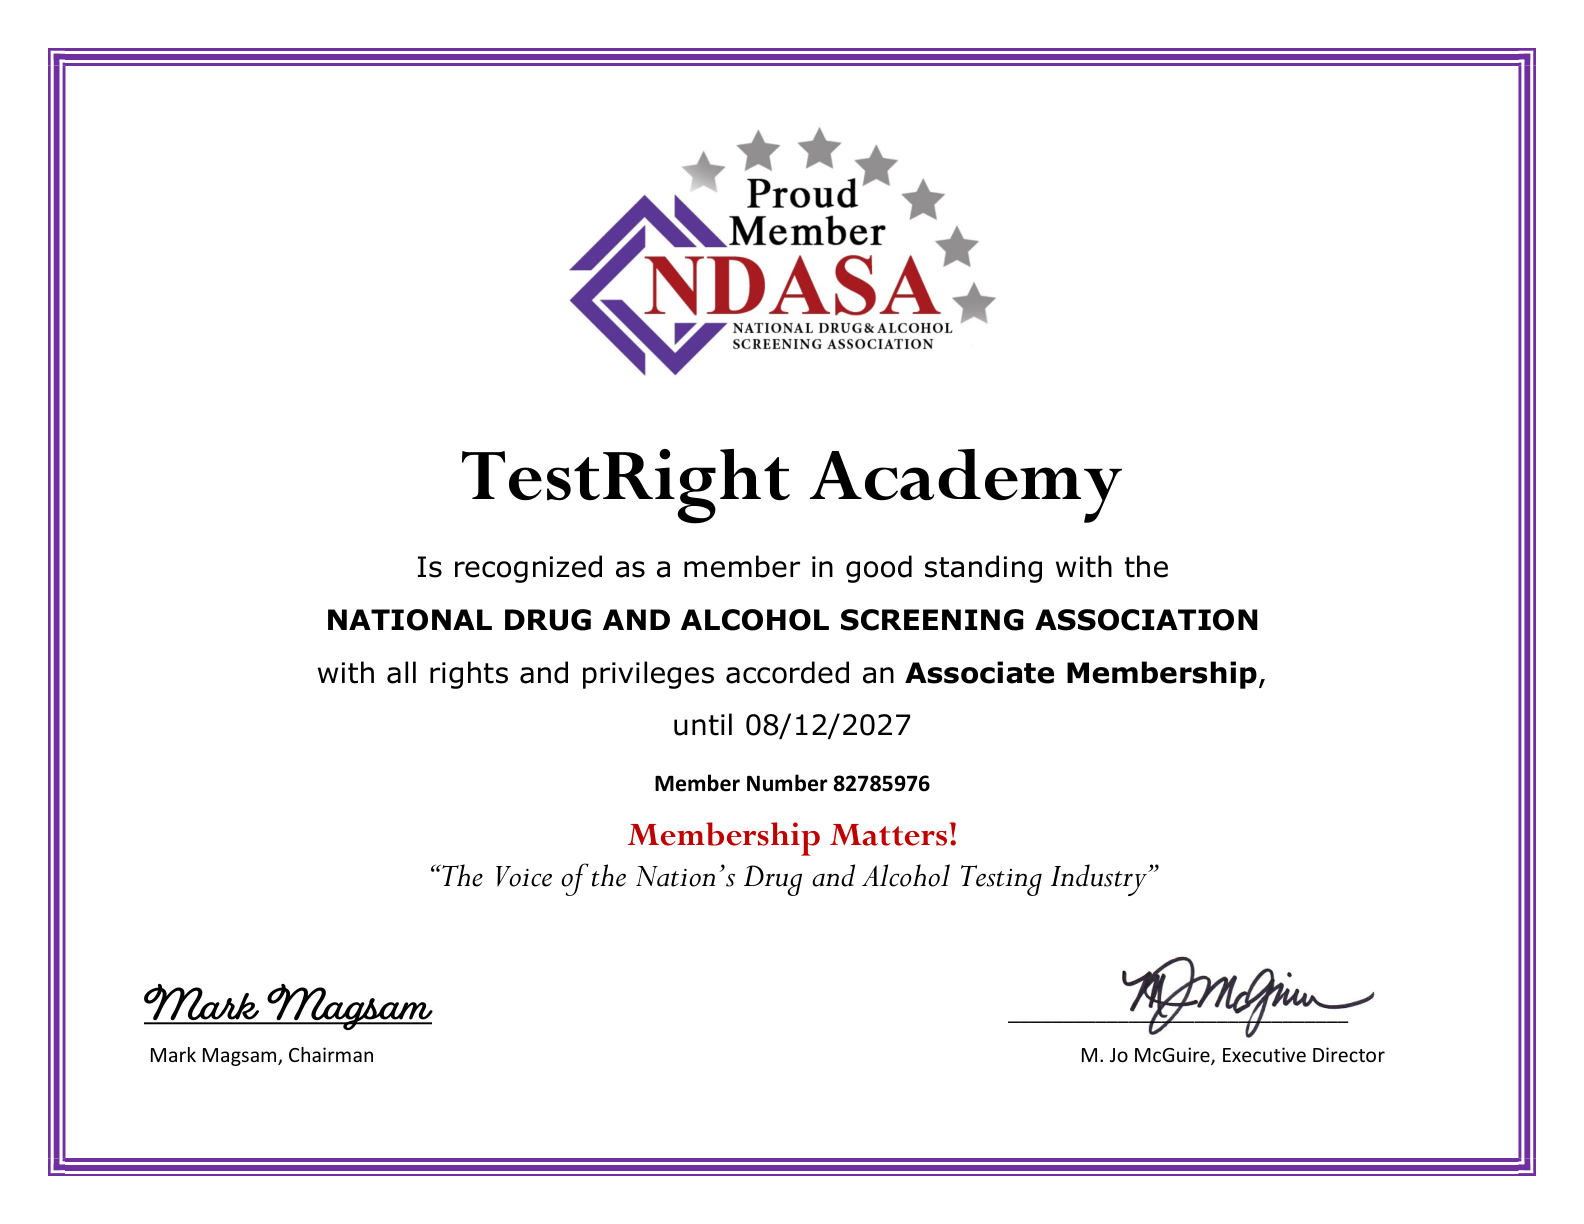
Industry membership only. NDASA membership is not a security certification, privacy audit, government approval, or endorsement of TestRight Academy’s technology.
Report a security concern
Found a potential vulnerability or have a security question? Email info@osegroupusa.com.
Questions
Something look wrong? .
Security, privacy and content concerns reach a person, not a queue.
Contact TestRight →